Help Desk: (651) 328-8905
Sales Inquiries: (651) 323-1775

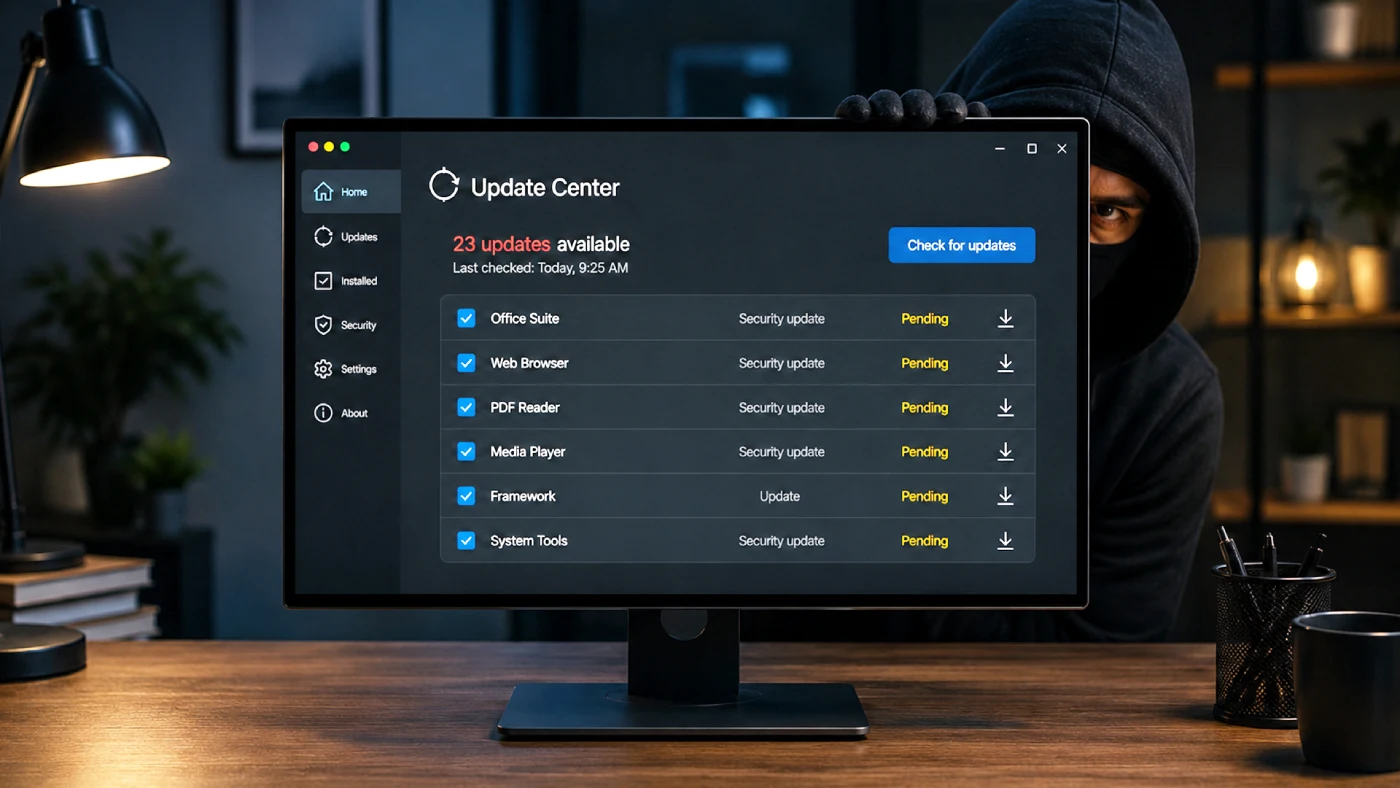
Unpatched Software Is Now the Number One Way Attackers Get In
For several years, the most common entry point for cyberattacks was stolen or compromised credentials. Multi-factor authentication addressed that path significantly. So attackers looked for another way in. According to the Verizon 2026 Data Breach Investigations Report, they found one, and it is one that many businesses are not sufficiently prepared for.
Quick Answer
Unpatched software has become the leading way attackers break into businesses, because known vulnerabilities stay open until updates are applied.
- Attackers scan for known, unpatched vulnerabilities constantly
- A missed update can leave a door open for months
- Patching every device by hand rarely keeps pace
- Automated patch management closes gaps consistently
- Updates are one of the cheapest, highest-impact defenses you have
The Shift to Vulnerability Exploitation
Vulnerability exploitation has now overtaken stolen credentials as the single most common initial access vector in breaches, accounting for nearly a third of all reported incidents.
A vulnerability is a flaw in software that can be exploited to gain unauthorized access. Software vendors find and fix these flaws regularly and release the fixes as updates. The problem is the gap between when a fix is released and when businesses actually apply it.
That gap is often significant. Many businesses fall behind on updates because the process is manual, requires downtime, or simply because nobody is actively managing it. Meanwhile, attackers know exactly when new vulnerabilities are disclosed because those disclosures are public.
How Attackers Exploit the Patching Gap
When a software vendor releases an update that fixes a known vulnerability, a predictable sequence follows. Security researchers analyze the fix to understand what flaw was addressed. That information spreads quickly. Cybercriminals build tools to exploit the flaw in systems that have not yet applied the update. Automated scanners run across the internet looking for machines still running the vulnerable version.The businesses that have not applied the update are now running software with a publicly known flaw and a working exploit in the hands of attackers. This can happen within days, or even hours, of an update release for high-profile vulnerabilities.
What to Do About It
The most reliable solution for small businesses is automated update management through a managed IT provider. Rather than relying on someone to manually check for and apply updates, a managed provider handles this on a regular schedule across all covered devices and systems.
For software that cannot be easily updated, additional monitoring, network segmentation, and restricted access can reduce the risk while a longer-term upgrade plan is developed. The goal is to make sure the gap between a fix being available and a fix being applied stays as small as possible.
Frequently Asked Questions
Why is unpatched software such a big risk?
Once a vulnerability is public, attackers actively scan for systems that have not applied the fix. Unpatched software is an open, known door.
What is patch management?
Patch management is the practice of keeping software and operating systems up to date across every device, ideally automated so nothing is missed.
How quickly should security patches be applied?
Critical patches should be applied as soon as possible after release. The longer a known vulnerability stays open, the greater the risk.
How can a small business keep up with patching?
Automated patch management through a managed IT provider keeps every device current without relying on manual effort that tends to fall behind.
Is your software up to date across every device and system your business relies on? If you are not certain, that uncertainty is worth addressing. Reach out and we will assess where your gaps are and how to close them.
Ready For A No-Nonsense Approach To IT?
Hire us to set your IT strategy up for sustainable success.
Learn about our proven No-Nonsense approach.
Get an IT roadmap designed specifically for you.
Fearlessly grow your business.
We Can Help
Call us at (651) 323-1775 or or fill out the form below.
Featured Posts
Unpatched Software Is Now the Number One Way Attackers Get In
For several years, the most common entry point for cyberattacks was stolen or compromised credentials. Multi-factor authentication addressed that path significantly. So attackers looked for another way in. According to the Verizon 2026 Data Breach Investigations Report, they found one, and it is one that many businesses are not sufficiently prepared for.
Quick Answer
Unpatched software has become the leading way attackers break into businesses, because known vulnerabilities stay open until updates are applied.
- Attackers scan for known, unpatched vulnerabilities constantly
- A missed update can leave a door open for months
- Patching every device by hand rarely keeps pace
- Automated patch management closes gaps consistently
- Updates are one of the cheapest, highest-impact defenses you have
The Shift to Vulnerability Exploitation
Vulnerability exploitation has now overtaken stolen credentials as the single most common initial access vector in breaches, accounting for nearly a third of all reported incidents.
A vulnerability is a flaw in software that can be exploited to gain unauthorized access. Software vendors find and fix these flaws regularly and release the fixes as updates. The problem is the gap between when a fix is released and when businesses actually apply it.
That gap is often significant. Many businesses fall behind on updates because the process is manual, requires downtime, or simply because nobody is actively managing it. Meanwhile, attackers know exactly when new vulnerabilities are disclosed because those disclosures are public.
How Attackers Exploit the Patching Gap
When a software vendor releases an update that fixes a known vulnerability, a predictable sequence follows. Security researchers analyze the fix to understand what flaw was addressed. That information spreads quickly. Cybercriminals build tools to exploit the flaw in systems that have not yet applied the update. Automated scanners run across the internet looking for machines still running the vulnerable version.The businesses that have not applied the update are now running software with a publicly known flaw and a working exploit in the hands of attackers. This can happen within days, or even hours, of an update release for high-profile vulnerabilities.
What to Do About It
The most reliable solution for small businesses is automated update management through a managed IT provider. Rather than relying on someone to manually check for and apply updates, a managed provider handles this on a regular schedule across all covered devices and systems.
For software that cannot be easily updated, additional monitoring, network segmentation, and restricted access can reduce the risk while a longer-term upgrade plan is developed. The goal is to make sure the gap between a fix being available and a fix being applied stays as small as possible.
Frequently Asked Questions
Why is unpatched software such a big risk?
Once a vulnerability is public, attackers actively scan for systems that have not applied the fix. Unpatched software is an open, known door.
What is patch management?
Patch management is the practice of keeping software and operating systems up to date across every device, ideally automated so nothing is missed.
How quickly should security patches be applied?
Critical patches should be applied as soon as possible after release. The longer a known vulnerability stays open, the greater the risk.
How can a small business keep up with patching?
Automated patch management through a managed IT provider keeps every device current without relying on manual effort that tends to fall behind.
Is your software up to date across every device and system your business relies on? If you are not certain, that uncertainty is worth addressing. Reach out and we will assess where your gaps are and how to close them.
Enroll in Our Email Course
Learn How a No-Nonsense IT Strategy Benefits Your ComBullet listpany:
Strategies to allocate your IT budget efficiently
Enhance cybersecurity defenses on a bButtonudget
Ensure your technology investments continue to serve your business as it grows
© Copyright 2026 RYMARK IT Navigation. Built in partnership with Tech Pro Marketing. | Privacy Policy

